Cyber threats no longer operate on predictable timelines. Attacks evolve in real time, often bypassing traditional defense layers before organizations can respond. In this environment, MSPs and software companies co-innovating for threat detection have become a practical necessity rather than a strategic option.
According to Statista, global cybercrime costs continue to rise, pushing organizations to rethink how they design and manage security systems. Internal teams alone often struggle to keep pace with the complexity of modern threats.
This is where MSPs and software companies working together changes things. They combine know-how about systems with deep product knowledge. Together they detect threats faster, respond better and keep adapting to new risks. This article explains how co-innovation in threat detection works and what to expect from these partnerships.
The Shift Towards Collaborative Threat Detection Models
From reactive defense to predictive systems
Traditional security models rely heavily on reactive measures. Alerts are triggered after an anomaly occurs, leaving a narrow window for response. MSPs and software companies co-innovating for threat detection are shifting this model towards predictive systems that identify patterns before incidents escalate.
By studying behaviour across many client systems, MSPs can spot early signs of a breach and act before systems are harmed.
Integration of infrastructure and application intelligence
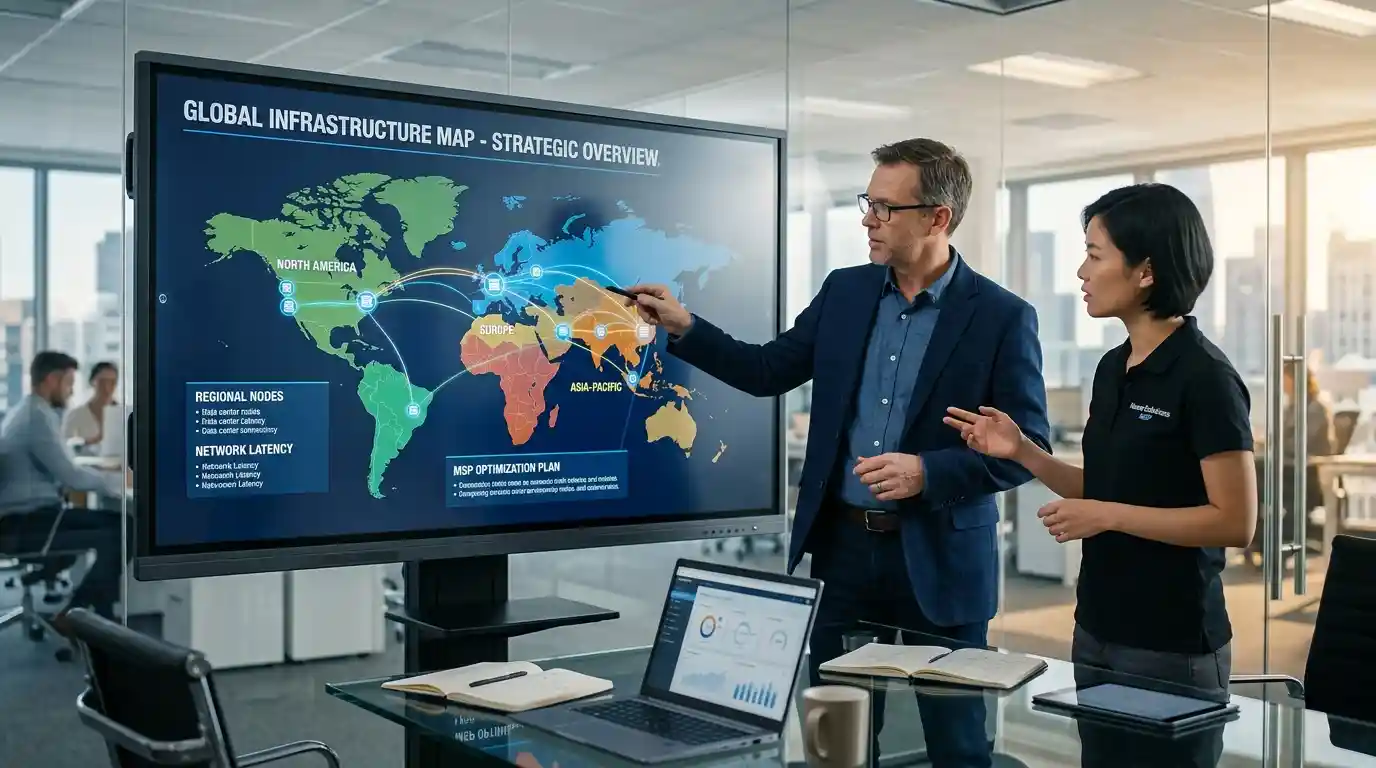
Software companies bring deep knowledge of application behavior, while MSPs manage infrastructure and network layers. When these insights are combined, organizations gain a more complete view of their threat surface.
Platforms such as the DiscoverMSPs directory help businesses find providers that can link these layers well.
Threat detection improves when data is shared across systems. MSPs operating across multiple clients can identify trends that individual organizations might miss. Software companies can then refine detection algorithms based on this data.
This cycle of shared intelligence strengthens defense mechanisms over time.
Role of MSPs in Advanced Threat Detection
Real-time monitoring and response
MSPs provide continuous monitoring across networks, endpoints, and cloud environments. This allows organizations to respond to threats as they emerge rather than after damage occurs.
Standards from groups such as NIST stress that constant monitoring is part of a mature security setup.
Incident management and remediation
Detection alone is not sufficient. MSPs manage the full lifecycle of incidents, from identification to containment and recovery. This reduces downtime and limits the impact of security breaches.
Infrastructure-level visibility
MSPs work at the system level. They can see network traffic, system logs and user activity. This wide view is key to spotting odd behaviour that may not show up inside a single app.
How Software Companies Strengthen Detection Capabilities
Application-level intelligence
Software companies design systems that generate valuable data about user behavior, system performance, and application usage. This data can be used to detect unusual patterns that indicate potential threats.
Research from CompTIA looks at why app-level security matters more in today's IT.
AI-driven threat analysis
Many software platforms now use AI to spot unusual activity. These systems sift through large amounts of data to find patterns that human analysts would struggle to see.
Integration with MSP systems
Effective co-innovation requires seamless integration between software platforms and MSP monitoring tools. This ensures that data flows freely between systems, enabling faster detection and response.
Benefits of Co-Innovation for Organizations
Faster detection and response times
When MSPs and software companies work together, detection processes become more efficient. Threats are identified earlier, and response actions are executed more quickly.
Improved accuracy in threat identification
Combining multiple data sources reduces false positives and improves detection accuracy. This allows security teams to focus on genuine threats rather than noise.
Scalable security solutions
Co-innovation lets firms grow their security as they grow. MSPs give the day-to-day support, and software companies supply tools that adapt.
Businesses looking for security partners that can grow with them often read DiscoverMSPs blogs to compare providers.
Looking for a verified MSP in your region? Browse the DiscoverMSPs directory to compare providers by service, location, and specialization.
Challenges in MSP and Software Collaboration
Data integration complexity
Integrating systems across multiple platforms can be complex. Differences in data formats and architectures may slow down implementation.
Alignment of priorities
MSPs focus on keeping things stable. Software companies focus on new product features. Lining these up takes clear communication and shared goals.
Maintaining transparency
Trust depends on transparency. Both parties must share data, insights, and performance metrics openly to maintain confidence in the partnership.
Frequently Asked Questions
How accurate is DiscoverMSPs’ data?
How often is DiscoverMSPs’ data refreshed?
1.What does co-innovation in threat detection mean?
It refers to MSPs and software companies working together to design, implement, and improve systems that detect and respond to cyber threats more effectively.
2.Why are MSPs important for threat detection?
MSPs provide constant monitoring, a view across systems and incident response. These help firms find and handle threats as they happen.
3.How do software companies contribute to threat detection?
Software companies provide app-level insight, data analysis and AI tools. These make detection more accurate and improve how teams respond.
4.What are the benefits of MSP and software collaboration?
The benefits are faster detection, better accuracy, security that grows with you and stronger protection against new threats.
5.Are these partnerships suitable for small businesses?
Yes, small businesses benefit from MSP partnerships as they gain access to advanced security capabilities without building large internal teams.
6.How can organizations choose the right MSP?
Judge MSPs on their skills, openness, security habits and how well they link with your current systems.
Conclusion
MSPs and software companies co-innovating for threat detection is a change in how firms handle cyber security. Instead of each working alone, security becomes a shared effort built on shared data and steady improvement.
Organizations that embrace this model are better equipped to respond to evolving threats while maintaining operational stability. The focus moves from reacting to incidents to anticipating them.
DiscoverMSPs helps firms find partners that support this approach, for stronger and more resilient security.
How to Implement MSP and Software Collaboration for Threat Detection
A step-by-step guide to building an effective threat detection system through MSP and software company collaboration.
Define Security Objectives
Identify key threat detection goals, compliance requirements, and risk areas before engaging with MSP and software partners.
Choose Compatible Partners
Select MSPs and software providers that can integrate systems and share data efficiently across platforms.
Implement Integrated Monitoring
Deploy tools that connect infrastructure and application-level insights for real-time threat detection.
Continuously Optimize Systems
Review performance, update detection models, and refine processes to adapt to evolving cyber threats.
 ChatGPT
 Claude
 Google AI Mode