A human security analyst working in a traditional SOC model cannot meaningfully review every alert generated by a 200-endpoint client environment, let alone a portfolio of 30 such clients. The economics of managed security services at SMB scale were already stretched before the alert volume inflection of the past few years. AI-powered security tools are the mechanism through which the best-performing managed service providers are resolving that tension: they are using machine learning-based detection and automated triage to manage alert volume at scale without proportional analyst headcount growth.
This is not theoretical. CompTIA’s cybersecurity research identifies AI-enhanced threat detection as the single fastest-growing capability investment among US managed security service providers in 2026. The MSSP market is differentiating on detection capability, not price, in the enterprise and upper mid-market segments. MSPs who have invested in AI-powered security tooling are winning these conversations. Those who have not are competing on price in a race they will not win. This article examines where the genuine AI security opportunities lie for MSPs, which tools are producing real results, and where the implementation risks are concentrated.
Where AI Is Genuinely Improving MSP Security Delivery
The hype around AI in security has produced plenty of vendor marketing that promises more than the tech can do. So start by knowing where AI really improves security for MSPs, and where it is mostly a label. That is the practical first step for any MSP thinking about AI security spend.
Behavioural threat detection in EDR
EDR platforms with machine learning that spots behaviour are the most mature and proven use of AI in MSP security. Old endpoint security matches known malware by its signature. Behaviour-based EDR looks at actions instead: new processes, file access, network links and registry changes that point to an attack, whatever the malware is. Zero-day and fileless attacks keep rising in client setups. For MSPs, behaviour-based EDR is not an upgrade on signatures. It is a different way of finding threats.
SIEM alert triage and correlation
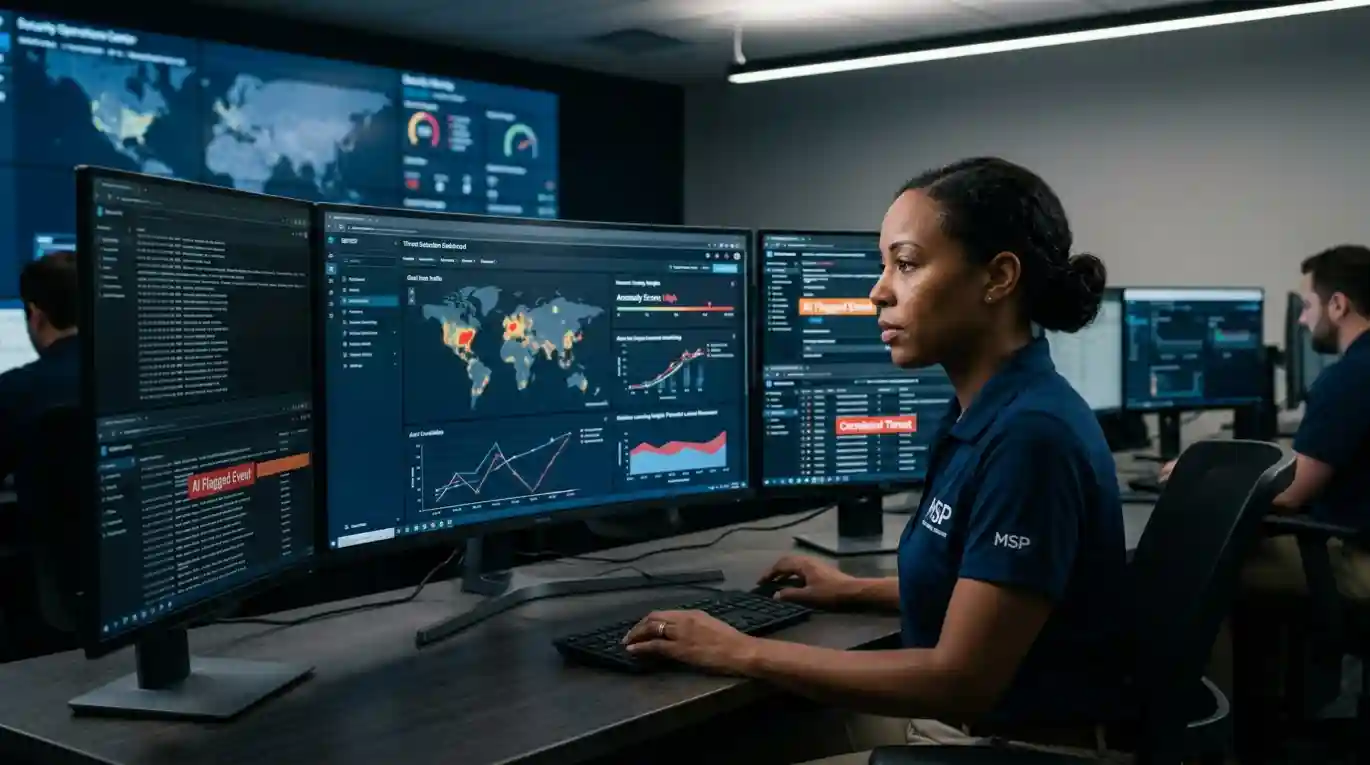
The alert triage problem in managed security is not primarily a detection problem. It is a prioritization problem. A well-tuned EDR and network monitoring deployment generates more alerts than any analyst team can review individually. AI-powered SIEM platforms apply machine learning to correlate alerts across data sources, identify which alert clusters represent genuine threat campaigns versus false positives, and prioritize analyst attention on the events most likely to represent active compromise.
The practical outcome is that analyst teams can handle more clients per FTE without sacrificing detection quality, which directly improves the economics of MSP-delivered security services. Compliance-focused security MSPs are finding that AI-driven SIEM correlation also improves the quality of compliance reporting, since correlated event data provides cleaner audit trails than raw alert logs.
Email security with large language model-based phishing detection
Phishing has changed faster than old rule-based email security can keep up. Business email compromise, targeted spear phishing with convincing stories and QR code phishing all slip past signature and reputation filters too often. That hurts MSPs whose clients judge them on phishing incidents. Email tools that use large language models to read what a message means, not just its headers and links, catch far more advanced phishing than rule-based tools. For MSPs judged partly on client phishing, this is the AI security spend with the biggest impact today.
Looking for MSPs with AI-powered security skills? Browse the DiscoverMSPs MSSP directory to compare providers by security stack and how they detect threats.
The New Revenue Streams AI Security Creates for MSPs
AI security tools do more than improve today's services. They open new services and new ways to price that did not make sense with older tech.
SOC-as-a-service at SMB price points
Building a traditional security operations center requires significant infrastructure investment, 24/7 analyst staffing, and management overhead that prices genuine SOC capability out of reach for SMB clients. AI-powered detection and automated response capability, delivered through a co-managed MSSP partnership, allows MSPs to offer meaningful SOC-grade threat monitoring to clients with 50 to 200 seats at price points those clients can sustain. The AI handles alert volume and initial triage; human analysts handle confirmed threats and client communication.
This model scales in a way that fully manual SOC operations do not, and it creates a premium security tier that generates meaningfully higher revenue per seat than basic monitoring.
Predictive vulnerability management
Old vulnerability management ranks fixes by CVE severity score. The problem is that not every critical flaw is equally likely to be used in a real attack. AI-powered tools add threat intelligence, real-world attack activity and each client's exposure. They produce a fix list ranked by real risk, so the flaws most likely to lead to a breach come first, not just those with the highest score. For MSPs, that is a stronger and provably better service that earns a premium over basic patching. Technographic data on DiscoverMSPs helps show which MSPs have built advanced vulnerability management into their standard offer.
AI-assisted threat hunting
Threat hunting, the proactive search for threat actor presence in environments that have not triggered automated alerts, has traditionally required specialized analyst skills that most MSPs do not have in sufficient depth to offer as a standard service. AI-assisted threat hunting tools that generate hypotheses based on behavioural data and guide analyst investigation have lowered the expertise threshold for structured threat hunting activity. MSPs who have invested in these tools can offer quarterly or bi-annual threat hunting engagements as a premium service tier, generating both additional revenue and the genuine security value of proactively identifying compromises that automated detection missed.
Where Implementation Risks Are Concentrated
AI security tools are not without implementation risks in MSP environments, and understanding where those risks concentrate is as important as understanding the opportunities.
False positive fatigue at scale
AI detection models that are well-calibrated for the training environments used during vendor development may generate elevated false positive rates in specific client environments. For an MSP managing a portfolio of diverse clients, a tool that generates even a modest false positive rate per client compounds across the portfolio into an analyst workload problem. Evaluating AI security tools against false positive rates in environments similar to the MSP’s client portfolio, rather than accepting vendor-published benchmarks from curated test environments, is essential before wide deployment.
Data privacy in AI security telemetry
AI security tools require access to client telemetry data: event logs, network flows, endpoint behavior data, and email content in some cases. MSPs who deploy these tools are transmitting client data to vendor AI systems for analysis. The data privacy implications of this transmission must be addressed in client contracts and vendor Data Processing Agreements before deployment, particularly for clients in regulated industries whose data is subject to GDPR, HIPAA, or other privacy frameworks. Failure to address this contractually creates both regulatory exposure and client trust risk.
The approach taken by the best-performing security-focused MSPs listed in DiscoverMSPs’ MSSP directory is to incorporate AI security tool data flows into their standard client Data Processing Agreements as a matter of course.
Frequently Asked Questions
How accurate is DiscoverMSPs’ data?
How often is DiscoverMSPs’ data refreshed?
1.How are MSPs using AI to improve security service delivery?
MSPs mainly use AI security tools for four jobs. They detect threats automatically in SIEM and EDR. They sort and rank alerts, so analysts are not swamped. They spot odd behaviour in client networks. And they respond automatically to simple incidents. The most mature setups pair machine learning with human analysts. AI handles volume and speed, while people make the hard calls.
2.What is the difference between AI-powered and rule-based security for MSPs?
Rule-based security spots known attacks through set signatures. It works on known threats but misses new methods. AI security uses machine learning to spot behaviour that breaks from a normal baseline, so it can catch attacks never seen before. For MSPs with many different clients, AI adapts to how each client normally behaves. Generic rules, by contrast, throw up too many false alarms.
3.What AI security tools are most relevant for MSPs in 2026?
The most useful AI security tools for MSPs in 2026 are five. AI-enhanced EDR that detects behaviour. AI-driven SIEM that links events and ranks alerts automatically. Network detection with machine learning that spots oddities. Email security that uses large language models to catch phishing. And AI-assisted vulnerability tools that predict which flaws will be used, rather than just list CVE scores.
4.What are the risks of deploying AI security tools in MSP environments?
The main risks are four. Too many false alarms if models are not tuned to each client. Model drift, where accuracy falls as setups change and the model is not retrained. Privacy issues from sending client data to vendor AI systems. And leaning too hard on automatic responses across many clients. The most important control is to test false alarm rates in setups like your clients' before you roll out widely.
5.How do AI-powered security tools create new revenue for MSPs?
AI tools open up new revenue for MSPs. They make SOC-grade detection affordable for small firms, which used to be too costly. They cut analyst hours per client for routine monitoring, which lifts margins on current contracts. And they set the MSP apart when clients compare how well providers detect threats. They also allow new services, such as AI-assisted threat hunting and predictive vulnerability management, that earn premium prices.
6.Should MSPs build or partner for AI security capabilities?
For most MSPs, partnering with AI security vendors is the right choice. Building your own AI models needs data scientists, large training data sets and ongoing upkeep. That only pays off at enterprise scale. Partnering with proven vendors, through co-managed or white-label deals, lets MSPs offer AI security without the build cost. They can then stand out on service quality and industry skill instead.
AI Security Is an Operational Necessity, Not a Feature
The alert volume problem in managed security environments is not going to resolve itself. Attack sophistication is increasing, client environments are growing more complex, and the volume of security events requiring triage will continue expanding. MSPs who continue delivering managed security through purely manual processes are building a cost structure that will either price them out of quality talent or out of the market on contract value.
AI-powered security tools are the mechanism through which the alert volume problem becomes manageable without proportional analyst headcount growth. The MSPs who have invested in these tools are not just improving their security delivery quality. They are building a cost structure and a service capability that competitors without AI investment will find increasingly difficult to match as the gap between AI-assisted and manual security delivery widens.
DiscoverMSPs provides verified data on MSPs with AI-powered security skills across the US, UK and global markets, sorted by tech stack and security specialty.
 ChatGPT
 Claude
 Google AI Mode