The average MSP deploys between eight and twelve separate security tools across their managed client environments. That statistic, drawn from CompTIA’s cybersecurity trends research, represents not a sign of thoroughness but a symptom of the reactive tooling accumulation that characterises security stack growth at most managed service providers. Each tool was added in response to a specific threat, a client requirement, or a vendor promotion. Few were selected as part of a deliberate integration architecture.
The result is a fragmented set of products that each generate their own alerts, require their own administrative interfaces, and produce security data that sits in disconnected silos rather than contributing to a unified threat picture.
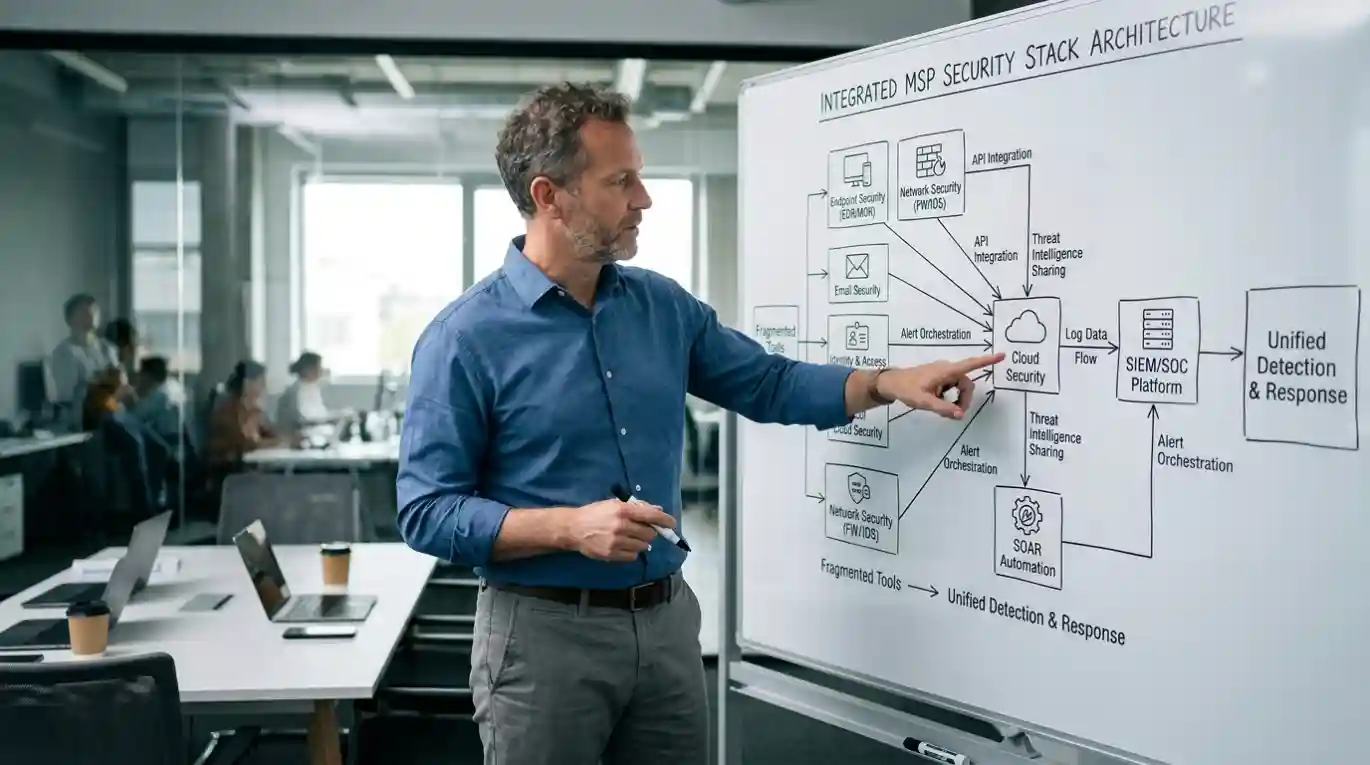
Building a coherent MSP security stack integration strategy is not about having fewer tools. It is about having tools that share data, reduce analyst context-switching, and produce correlated intelligence rather than isolated alerts. The security-specialised MSPs who consistently outperform on threat detection and incident response are those who have invested in integration architecture, not just in individual tool quality. This guide covers the principles of MSP security stack design, the integration decisions that matter most, and the consolidation approach that produces the best operational outcomes.
Why Security Stack Fragmentation Undermines MSP Security Delivery
The operational cost of security stack fragmentation is rarely quantified but consistently felt. Analysts who must log into eight separate consoles to investigate a single incident are not providing inferior service through lack of effort. They are working within an architecture that structurally prevents them from doing their jobs efficiently.
The correlation gap
The most dangerous consequence of fragmented security stacks is the correlation gap: the space between disparate security tools where an attacker can operate without triggering alerts in any individual system. An initial access event detected in endpoint telemetry, lateral movement visible in network flow data, and credential abuse logged in an authentication platform represent a coherent attack sequence when correlated. In a fragmented stack where these data sources sit in separate systems without automated correlation, they appear as three unrelated low-priority alerts. The attacker reaches their objective while the MSP’s team processes each alert in isolation and finds nothing actionable.
Analyst context-switching overhead
Every time an analyst must switch between security consoles to gather context for an alert investigation, they lose time and risk losing the thread of the investigation. In a fragmented stack with multiple unintegrated tools, investigating a complex alert can require context-switching between five or six interfaces, each requiring separate authentication, each presenting data in a different format, and each lacking the context that the other tools hold. The mean time to investigate and respond to security incidents in fragmented stack environments is measurably higher than in well-integrated environments, which directly affects the service quality delivered to clients.
The Core Components of a Well-Integrated MSP Security Stack
A working MSP security stack in 2026 does not need every security tool on the market. It needs the right tool in each security area. Choose each one on how well it links with the rest, as well as how well it detects threats.
EDR as the detection foundation
Endpoint detection and response is the primary data source for most security investigations in managed client environments. The EDR platform an MSP deploys should offer native integration with the PSA and RMM tools that form the MSP’s operational core, multi-tenant management capability that allows MSP analysts to monitor all client environments from a single console without client data cross-contamination, and an API that allows alert data to flow into the SIEM for correlation.
EDR platforms that require separate per-client deployments, lack native PSA integration, or do not expose their alert data via API create integration debt that accumulates over time and limits the MSP’s ability to build a coherent security architecture around them.
SIEM as the correlation layer
The SIEM is where the correlation gap problem is solved or left unsolved. A SIEM that ingests data from EDR, network monitoring, email security, authentication logs, and DNS filtering creates a single correlated view of security events across the client environment. A SIEM that only ingests data from one or two sources is a log management tool, not a correlation platform.
MSPs evaluating SIEM platforms should assess the breadth of native integrations, the quality of the correlation rules provided out of the box versus requiring custom rule development, and the scalability model for pricing across a multi-client MSP environment. Compliance-focused security MSPs additionally need SIEM platforms that produce compliance-ready report outputs, not just raw alert data.
Identity and access management integration
Identity attacks are the most common way in today. They include stolen logins, business email compromise and gaining higher access. A stack that does not feed identity data into its SIEM has a big blind spot. Linking the MFA platform, the directory and the SIEM lets you spot login abuse, impossible travel and access grabs. Without identity data, you cannot see them. The NIST Zero Trust Architecture publication says plainly that identity is the main control point in Zero Trust. So your stack must treat identity data as key threat input, not an admin afterthought.
Looking for MSPs with integrated security stack capabilities? Browse the DiscoverMSPs MSSP directory to compare providers by security architecture and technology stack depth.
The Vendor Consolidation Question
Security vendor consolidation has been an active trend in the MSP market for several years, driven partly by the operational benefits of integration and partly by the commercial pressure that managing many vendor relationships creates. The practical question for MSPs is not whether to consolidate but which consolidation path produces the best outcome for their specific client portfolio.
Platform vendors versus best-in-class point solutions
Big security vendors, including Microsoft, CrowdStrike, Palo Alto Networks and SentinelOne, each offer platforms that cover several security jobs in one console. The link benefit is real. Tools from one vendor share a data model, connect events automatically and are run from one screen. The trade-off is that each tool may not match the best single product for that job. MSPs must decide whether the benefit of linked tools outweighs the gaps, for the threats that matter most to their clients. For more on this trend, see Gartner’s security vendor consolidation survey.
Integration through open APIs
MSPs that prefer the best tool for each job can link them through open APIs instead. SOAR platforms, orchestration tools and SIEMs with many ready-made connectors can join separate tools into one data flow, with no need for a single vendor. Building and keeping up this link layer takes real effort. Count that effort alongside licence costs when you choose tools. SaaS resellers and ISVs in the MSP market who specialise in security links can speed this work up a lot.
Frequently Asked Questions
How accurate is DiscoverMSPs’ data?
How often is DiscoverMSPs’ data refreshed?
1.What should an MSP security stack include in 2026?
A well-built MSP security stack includes behaviour-based EDR, a SIEM to manage logs and link alerts, advanced email security, DNS filtering, risk-based vulnerability management, MFA management and backup with immutable storage. For compliance-focused MSPs, add a compliance platform that maps controls to NIST CSF, ISO 27001 and SOC 2. It gives clients the reports they need for audits.
2.What is the security stack fragmentation problem for MSPs?
A security stack splinters when an MSP collects tools from many vendors that do not link well. Security data spreads across separate platforms. Analysts jump between consoles. Alerts cannot be connected. And managing many vendors piles up work. A splintered stack is harder to run, costs more to keep and detects threats less well than a joined-up one.
3.How should MSPs approach security vendor consolidation?
Map your current security tools against what your service needs. Find which tools add the most value and which create the most admin. Then ask whether a major platform, whose tools already link, could replace several single tools. The goal is a setup where data moves between tools with no manual work, and analysts work from one screen, not many.
4.How does PSA and RMM integration affect MSP security stack decisions?
Security tools that link directly with PSA and RMM platforms cause far less friction than tools that need separate logins and manual exports. Tools that open PSA tickets for threats automatically, connect security events to RMM asset data and let you fix things from one screen cut response times across all clients. Make PSA and RMM links a top test for any security tool you buy.
5.What is the right security stack for a small versus large MSP?
Small MSPs with fewer than 500 managed seats usually do best with one platform. A single vendor covers EDR, DNS filtering and SIEM, topped up with the best email security and backup. That keeps admin low on a tight budget. Larger MSPs with thousands of seats can afford the best single tool for each job, and invest in the links that join them.
6.How do MSPs ensure their security stack covers the NIST Cybersecurity Framework functions?
MSPs can map their stack against the five NIST CSF functions: Identify, Protect, Detect, Respond, and Recover. Asset and vulnerability management address Identify. EDR, MFA, and DNS filtering address Protect. SIEM and network monitoring address Detect. Incident response runbooks and automation address Respond. Backup and disaster recovery address Recover. Gaps in any function represent both security risk and a compliance gap for clients whose audit frameworks reference NIST CSF.
Integration Is the Architecture Decision That Matters Most
The security tools an MSP deploys matter less than how they are integrated. A fragmented stack of best-in-class tools that do not communicate produces worse security outcomes than a well-integrated stack of competent tools that share data and enable correlated analysis. This is the counterintuitive truth that most MSP security stack decisions miss: the selection decision for each individual tool matters far less than the integration architecture decision for the whole.
A joined-up MSP security stack needs three things. Treat links as a first test, alongside detection quality and price. Invest in the SIEM or SOAR layer that connects events across tools. And commit to steadily cutting the number of tools, so admin falls over time rather than grows. MSPs that do this respond faster, detect better and use analysts more efficiently.
DiscoverMSPs provides verified data on MSPs with joined-up security stacks, sorted by tech platform, security design and service model.
 ChatGPT
 Claude
 Google AI Mode