Software security is now too complex and too specialised for most dev teams to handle alone. Code scans, tests on running apps, checks on open-source parts, container scans and runtime protection each need special skills, tools and steady discipline. That competes head-on with the push to ship features. So at most mid-size software firms, the security programme looks complete on paper but is patchy in practice. Tools are installed but not managed. Scans are set up but not reviewed. Findings are logged but not fixed.
Bringing an MSP into your software security stack closes this gap. MSPs that specialise in app security bring the steady discipline and skills that busy dev teams cannot keep up. This guide explains why this differs from bringing in an MSP for infrastructure. It covers what the setup should look like, how to set roles so nothing overlaps or falls through, and the most common ways it fails. The DiscoverMSPs MSSP directory lists app security providers whose skills reach into software security.
Why Software Security MSP Integration Differs From Infrastructure Integration
Most firms that hire MSPs do so for infrastructure: networks, endpoints, cloud and help desk. Software security needs a very different model. Here the MSP takes part in a workflow, the way software is built and shipped. It is not just running infrastructure that exists apart from that work.
The CI/CD pipeline as the integration point
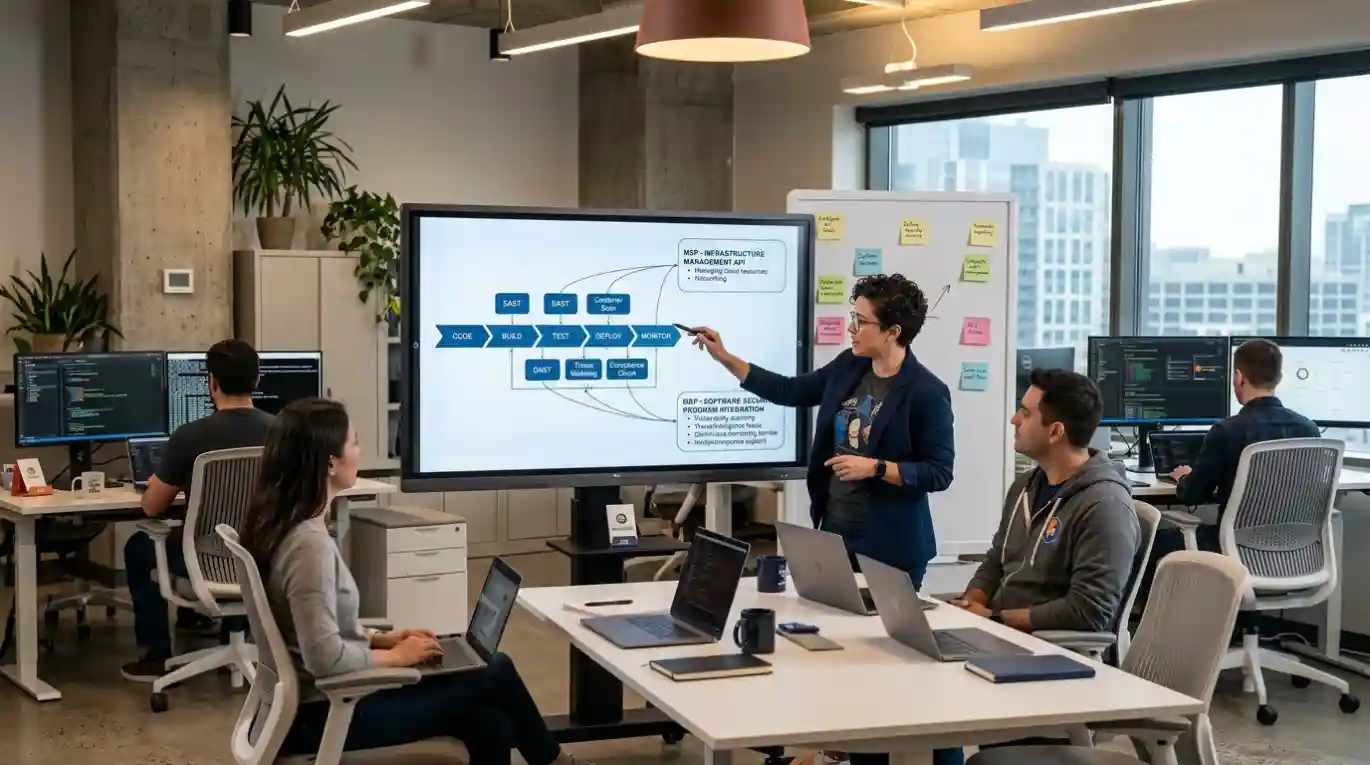
In a software security-integrated MSP model, the MSP’s presence in the security program is felt most directly in the CI/CD pipeline. Security gates in the pipeline that block deployments when critical vulnerabilities are detected in SAST or SCA scans need to be managed with the operational discipline of any production system: false positive rates need to be monitored and tuned, severity thresholds need to be appropriate to the specific codebase and risk context, and the MSP needs to be responsive to developer questions about findings in a way that supports rather than obstructs the development workflow. An MSP who manages these gates without developer empathy creates the conditions for security gate bypass, which eliminates the security value entirely.
The OWASP reference framework
Software security MSPs that follow known frameworks give clients a clear way to judge how complete their programme is. One such framework is the OWASP Application Security Verification Standard. The ASVS sets checks at three levels of assurance. So the MSP and client can agree a target level that fits the app's risk before work starts. That beats vague “best practice” reviews, which give uneven results that are hard to compare over time.
The Integration Architecture for Software Security MSP Engagement
To bring an MSP into a software security programme well, decide on tool access, data flows, roles and communication before the MSP starts. Do not find these out through friction once the work is under way.
SAST and DAST tool access models
Static and dynamic application security testing tools require the MSP to have access to scan results, the ability to configure scan parameters for specific applications, and in some models the ability to trigger scans in response to code changes or scheduled intervals. Access should be provisioned through dedicated service accounts with scopes limited to the functions the MSP performs. Administrative access to the security tools should not be granted unless the MSP’s role explicitly includes tool administration.
Most SAST and DAST platforms expose their findings through APIs, which allows integration with the MSP’s vulnerability management platform for centralized tracking without requiring MSP engineers to work directly in the client’s development tooling environment.
Software composition analysis and dependency management
Software composition analysis tools that identify open-source dependency vulnerabilities generate large volumes of findings that require consistent triage methodology to be actionable. An MSP managing SCA findings needs to distinguish between vulnerabilities in direct dependencies that are exploitable in the application context, transitive dependency vulnerabilities where the vulnerable code path is not reachable, and false positives where the CVE affects a code path that the application does not exercise.
Without this triage layer, raw SCA outputs overwhelm development teams with findings they cannot prioritize, which produces the same security paralysis as no SCA program at all. MSPs with compliance governance expertise understand that SCA output also feeds supply chain security compliance requirements, making triage quality a compliance matter as well as a security one.
Runtime security monitoring for production applications
Runtime protection and cloud workload tools watch live apps for attacks, odd behaviour and attempts to exploit them. This layer needs the most carefully set roles, because a runtime alert can trigger responses that take production down. Before monitoring starts, agree clearly whether the MSP may act on its own in production, or must flag events for your team to decide. Security-specialised MSPs with mature runtime playbooks know this and will usually raise it during onboarding.
Looking for MSPs that can join your software security work? Browse the DiscoverMSPs MSSP directory to compare providers by app security focus and DevSecOps skills.
The Most Common Software Security MSP Integration Failure Patterns
Software security MSP integration fails in predictable ways, and understanding the failure patterns before beginning the engagement allows both parties to structure the relationship to avoid them.
Undefined remediation ownership
The most common failure pattern in software security MSP engagements is undefined remediation ownership. The MSP identifies vulnerabilities. Nobody owns the process of ensuring they are fixed. Findings accumulate in the vulnerability management platform unassigned, unfixed, and eventually deprioritised in favor of new feature development. The MSP reports findings volume correctly; the organization’s actual security posture does not improve. Preventing this requires explicit assignment of remediation ownership for each vulnerability category before the engagement begins, with escalation paths and SLAs that the MSP is responsible for enforcing.
Developer alienation
Security and dev teams have often clashed. MSPs that run security tools without knowing how developers work tend to make that worse. Findings written in security jargon with no code context, severity scores that ignore how exploitable a flaw really is, and gates that block a release with no fix advice all push developers away. That weakens the whole programme. MSPs that treat developers as partners, not compliance targets, get faster fixes and a better security culture over time.
Frequently Asked Questions
How accurate is DiscoverMSPs’ data?
How often is DiscoverMSPs’ data refreshed?
1.Why do enterprises integrate MSPs into their software security stacks?
Firms bring MSPs into their software security stack to fill app security gaps they cannot fill cheaply themselves. App security MSPs bring code scans, live app tests, open-source checks and pen testing. These are costly to build in-house, especially for mid-size firms whose output does not justify a full-time app security team.
2.What is the difference between infrastructure and software security MSP integration?
An infrastructure MSP manages networks, endpoints and cloud. A software security MSP takes part in how software is built and shipped. It reviews code for flaws, runs the app security tools, watches live apps for threats and acts as a security gate in CI/CD pipelines. That needs different tools, skills and access from infrastructure work.
3.What access does an MSP need to integrate into a software security stack?
MSP software security integration typically requires API access to SAST and DAST platforms for findings management, read access to CI/CD pipeline configurations to monitor security gate events, access to dependency scanning tool outputs, and integration with the vulnerability management platform for remediation tracking. Access should be scoped to the minimum required for each function, documented in the service agreement, and reviewed on a defined cadence.
4.How do MSPs manage findings from application security testing tools?
An MSP handling app security findings pulls reports from code scans, live tests and open-source checks into one place. It sorts them by severity and how exploitable they are. It assigns fixes to the right owners, tracks them against agreed SLAs and reports on flaw numbers at set times. Its value is a steady way of sorting, skill at ranking fixes and the tracking and escalation that busy dev teams often drop.
5.What role boundaries should be defined for MSP software security integration?
Role boundaries should cover: which tools the MSP manages versus internal ownership, who makes final triage and severity rating decisions, who communicates findings to development teams, what the MSP’s authority is to escalate unresolved vulnerabilities, and what happens when the MSP and internal security team disagree on risk acceptance. A RACI document covering these functions should be agreed before access is provisioned.
6.How do enterprises evaluate MSPs for software security stack integration?
Judge MSPs on five things. Do they know your exact scan and test tools? Have they run app security for teams your size? Can current clients vouch for them inside a software security workflow? How secure is their own development? And how do they handle false alarms and talk to developers? How well they talk to developers is the best sign of long-term success.
The Integration Is the Program
A software security MSP engagement that is poorly integrated into the development workflow is not a security program. It is a compliance theatre exercise that generates reports without improving the security of software leaving the organization. The integration architecture decisions covered in this guide, role boundaries, access models, CI/CD integration, developer communication protocols, and remediation ownership, are not peripheral details. They are the program.
MSPs who understand this bring implementation frameworks that address these decisions upfront rather than discovering them through operational friction. Enterprises who evaluate MSPs on integration architecture capability as well as technical security knowledge consistently build more effective software security programs than those who evaluate purely on tool knowledge and past client references.
DiscoverMSPs provides verified data on MSPs that work in app security and software security stacks, sorted by tech focus and DevSecOps experience.
 ChatGPT
 Claude
 Google AI Mode