Finding mssp companies in usa is not hard because there is no information. It is hard because there is too much scattered, stale, and inconsistent information. If you have spent any time building channel marketing campaigns or directing B2B sales teams in the cybersecurity sector, you know this frustration intimately. I have watched countless teams start quarter after quarter with high expectations, only to find themselves wasting weeks manually sorting through unverified directories or cold-calling firms that are entirely the wrong fit.
This happens because of a structural flaw in how channel intelligence is typically gathered. Today, security vendors and channel teams are no longer looking for “any provider”. They are looking for the right provider based on country, security focus, services offered, client fit, business size, technology stack, and partner-readiness. A broad, untargeted approach simply burns through your operating budget and damages your brand reputation among potential partners who expect you to understand their business before you reach out.
To build a strong partner programme, you need to understand how these firms work day to day. MSSPs usually cover SOC work, MDR, endpoint protection, cloud security, firewalls, vulnerability management, compliance, threat monitoring, incident response and cutting cyber risk. They sit at the most critical point of their clients' risk plans. The pressure on them is huge. To see what is expected of them, read the CISA guidance for managed service providers and customers. It shows how high the modern security bar has become.
Because of this intense pressure, MSSP leaders do not have time to educate vendors during a pitch. They need technology partners who already understand their specific service delivery model. This is exactly why relying on a verified data platform such as DiscoverMSPs has become a fundamental necessity. Instead of guessing, revenue teams can use structured intelligence to confidently shortlist better-fit managed security service providers worldwide.
Why Finding MSSP Companies in USA Has Become More Complicated
The cybersecurity channel ecosystem has evolved rapidly over the last decade. Historically, a software vendor could run a basic search for an mssp usa, download a static contact list, and hand it to a sales development team to start dialling. Today, applying that outdated method is a guaranteed recipe for terrible conversion rates. The market has fractured into highly specialised niches, and identifying the top managed security service providers requires far more strategic nuance.
When you look closely at why outreach campaigns fail to generate pipeline, the root cause almost always points back to a lack of data depth. A sales team may struggle because:
- Some providers call themselves MSPs but only offer light security support.
- Some MSSPs focus only on compliance-heavy industries.
- Some firms serve local SMBs while others support enterprise accounts.
- Some lists are outdated before a campaign even starts.
- Some databases lack detail on services, location or tech stack.
Let us examine why these friction points exist. The distinction between a standard managed IT provider and a true security provider is frequently blurred in marketing materials. Many traditional IT firms have added basic antivirus or firewall management to their portfolio and subsequently rebranded themselves to capture higher-margin security revenue. However, if your product is an advanced threat hunting platform or an enterprise-grade MDR solution, these lightly equipped providers will lack the mature security operations centre required to manage your technology. Sending them a partnership proposal is a mutual waste of time.
Similarly, industry specialisation creates rigid boundaries within the channel. A managed security service provider that built its entire business around healthcare compliance and medical data regulations will operate very differently from one focused strictly on the defence industrial base. Their internal skill sets, technology stacks, and procurement cycles are strictly tailored to those regulatory environments. If you are targeting MSSP companies in USA, you must segment your outreach by the exact vertical markets they are equipped to serve.
Client size is another key factor that shallow data misses. An MSSP protecting local fifty-person law firms faces very different problems from one securing global logistics firms. The smaller provider usually wants simple, low-cost rollouts. The enterprise provider needs complex links, custom API access and setups that scale. If your data does not tell these two apart, your team will keep pitching the wrong value.
Then there is the issue of data decay, which is arguably the most silent drain on channel productivity. The managed services sector experiences constant mergers, private equity acquisitions, and leadership turnover. A list of managed security service providers that was considered accurate six months ago is likely filled with dead email addresses, obsolete company names, and departed executives today. When teams rely on static lists, they spend more time managing email bounce rates than having meaningful commercial conversations.
Finally, standard firmographic data is no longer sufficient to qualify a modern security partner. Knowing a company’s revenue bracket and employee count is helpful, but knowing their exact technology stack is transformative. If your software integrates natively with a specific remote monitoring tool or endpoint protection platform, you need to know which providers use those tools before you pick up the phone. Without this level of technographic and service-level depth, vendors are forced to ask basic qualification questions that should have been answered well before the first point of contact.
What Should a Reliable List of Managed Security Service Providers Include?
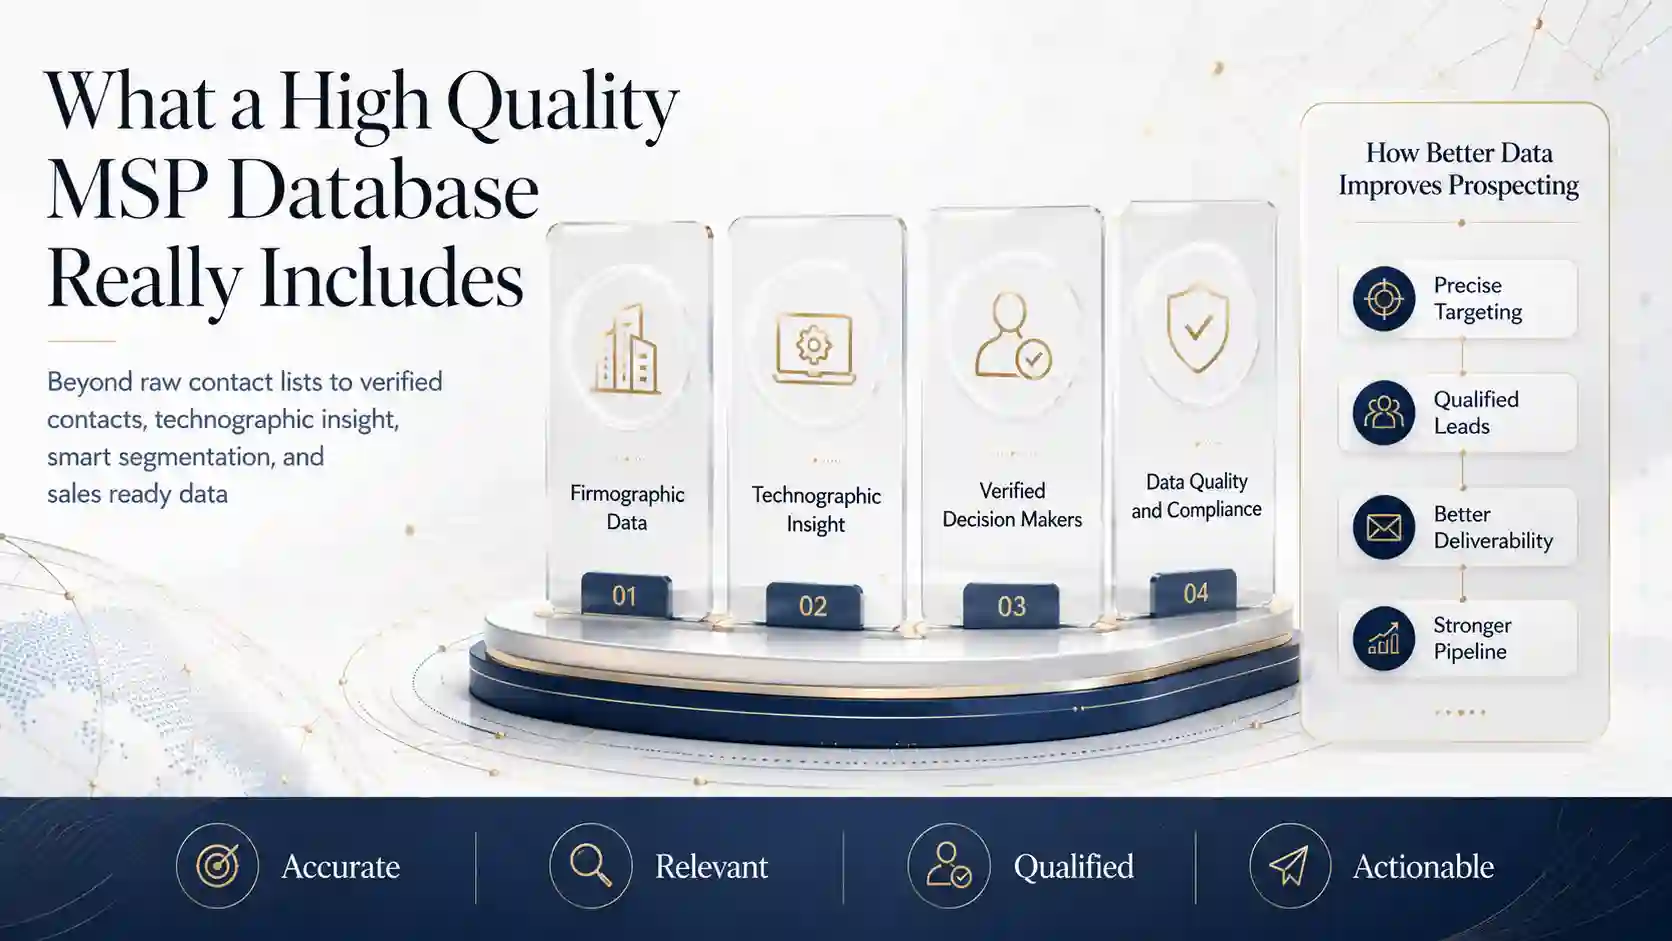
A useful list is not just company names and websites. It should help a sales, marketing, channel, or investment team understand whether each MSSP is worth pursuing. When evaluating data sources, you must look far beyond basic contact details. A generic directory might tell you that an organisation exists, but it will completely fail to tell you how that organisation operates. If your revenue operations or partner recruitment teams cannot see the operational architecture of a target provider from the data alone, they will still spend hours manually auditing websites before writing a single email.
A serious managed security service providers database should include a detailed company profile, verified location, exact staff size, markets served, main security services, decision maker contacts where available, company details, service type and CRM-ready format. That level of detail lets you split your market precisely. For example, whether a firm runs its own security centre or resells a white-label service changes your whole pitch. A message to an independent, top-tier defender must be very different from one to a hybrid regional firm.
Before trusting any MSSP list, check whether it helps you answer:
- Is this provider truly security-led or mainly an IT support firm?
- Which country or region does it serve?
- Does it work with SMBs, mid-market firms, or enterprise clients?
- Does it offer MDR, a SOC, compliance, cloud security, endpoint protection or vulnerability management?
- Is the data recent enough for outreach?
- Can the list be filtered for campaign fit?
- Can the data be reviewed through a sample before purchase?
If the data provider cannot answer these questions with confidence, you are probably looking at scraped public data packaged for a quick sale. In high-stakes B2B work, unverified lists can cause real problems. For campaigns across North America, it is wise to align your filters with known expectations. The Canadian Centre for Cyber Security guidance on managed service providers explains the security standards serious providers must meet. Those should match the categories you filter for in your list.
How Do You Find the Right MSSP USA Data Without Wasting Weeks?
A typical broad web search for an mssp usa can yield thousands of names, but it rarely delivers actionable buying intelligence. A team that relies solely on search engine scraping or entry-level business directories will inevitably hit a wall. They will still need to manually clean the data, verify the contacts, remove irrelevant firms, and organize the accounts by service fit. This tedious administrative process eats up valuable weeks of a campaign, stalling momentum and delaying pipeline generation.
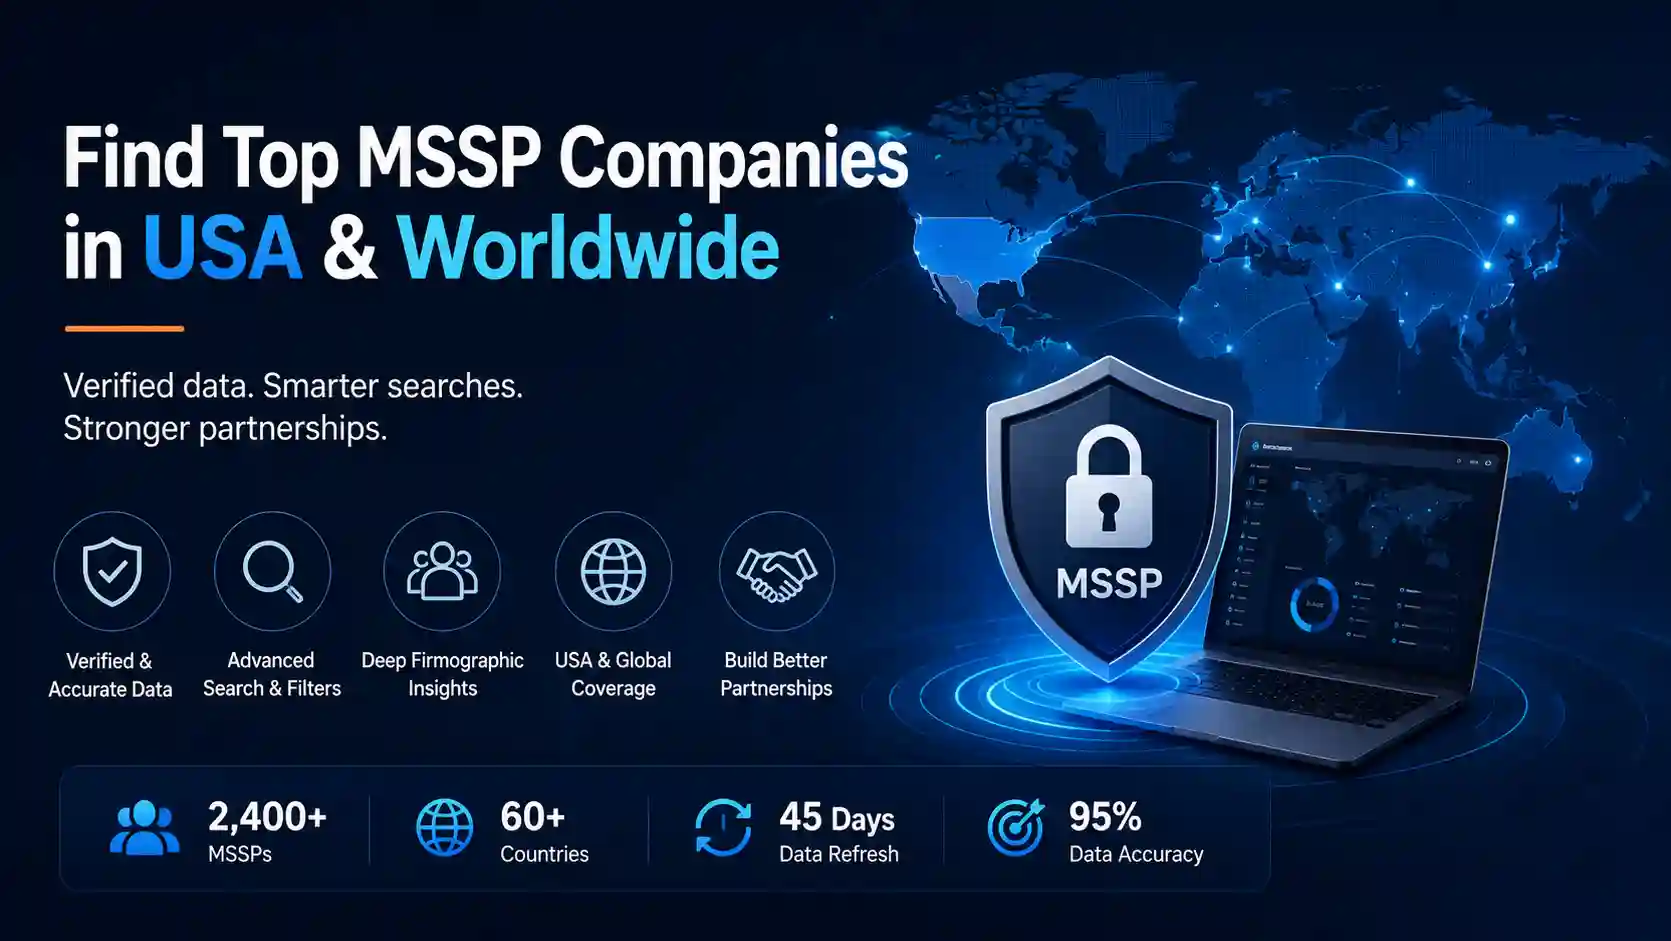
This specific bottleneck is why specialist intelligence platforms have become so vital for modern commercial strategy. A platform like DiscoverMSPs helps vendors, investors, and sales teams find MSSPs by country, security category, technology focus, and business profile. Rather than functioning as a rigid, static list, an intentional MSP database serves as a dynamic filtering engine. It allows a business development manager to strip away the noise of general IT firms and isolate the exact subset of top managed security service providers that match their technology stack or geographic requirements. This targeted approach transforms data acquisition from a painful, multi-week cleanup project into a clean, strategic workflow.
When building out your go-to-market data strategy, a structured, repeatable process ensures your team remains efficient and compliant. A good workflow looks like this:
- Define the exact buyer profile before searching.
- Choose target markets such as USA, Australia, Canada, and selected global regions.
- Tell apart MSPs, MSSPs, hybrid MSP-MSSPs, VARs and security consultancies.
- Shortlist based on service focus and commercial fit.
- Validate the sample before scaling outreach.
- Keep compliance and opt-out processes clear.
By maintaining this systematic approach, you prevent your sales pipeline from being contaminated with low-quality or completely irrelevant leads. The objective is to build a highly targeted list where every single account has a logical, demonstrable reason for being included. This level of focus protects your domain reputation, improves your response rates, and respects the time of the security professionals you are trying to reach.
Once the list is clear, the next challenge is trust. Buyers need to know why a newer specialist platform may be more useful than an older, broader database.
Can You Trust a Specialist MSSP Data Platform Over an Older General Database?
When building your market strategy, it is entirely reasonable to ask whether a niche intelligence tool is actually necessary. Older, well-established B2B databases have been the backbone of sales operations for decades, and they certainly still hold value for broad, horizontal prospecting. If you need to map out every manufacturing firm in a specific postal code to sell general office supplies, a generalist data provider will serve you well. However, attempting to locate high-calibre mssp companies in usa requires a much sharper, more deliberate lens.
The primary limitation of a general database is structural. It usually only confirms that a company exists and falls roughly into a broad IT or technology category. A specialist MSP and MSSP data platform, by contrast, is engineered to help a buyer understand exactly what kind of provider it is, where it operates, what specific services it offers, and whether it represents a realistic fit for a channel or direct sales campaign. In channel marketing, context is everything. Knowing a company has fifty employees is useless if you do not know whether those employees are managing local helpdesks or running a complex incident response unit.
Why Specialist Data Matters in the MSSP Market
The security channel is too complex for shallow labels. Revenue leaders need deep context before they spend budget on outreach.
- MSSPs are not all built for the same buyer.
- Cybersecurity service categories change quickly.
- Many providers use overlapping labels such as MSP, MSSP, MDR provider, SOC partner, cloud security consultant, or compliance advisory firm.
- A campaign built on weak segmentation wastes sales effort.
- A specialist list can help teams focus on accounts with clearer service and market fit.
Relying on generic labels makes it nearly impossible to identify the top managed security service providers for your specific product integration. You need distinct indicators, such as detailed technographic data, to see the infrastructure these firms are already deploying and defending. Without that visibility, you are essentially pitching in the dark.
How Can I Make Sure DiscoverMSPs Provides the Right MSSP Data?
My most direct advice to any channel leader is never to trust any database blindly, regardless of the brand name or reputation attached to it. The only responsible approach to data procurement is to review a tangible sample, scrutinise the available data fields, compare those records against your internal ideal customer profile, and confirm that the intelligence actually supports your intended campaign use.
If you are evaluating your options, it is helpful to look closely at About DiscoverMSPs. The platform presents itself as a dedicated MSP and IT channel intelligence solution built specifically to help vendors identify, qualify, and engage partners. Its stated mission is to remove guesswork from channel sales, combining human-verified research with machine-validated updates. This is exactly the dual-layer approach you should look for when sourcing a reliable list of managed security service providers. A machine can scrape a website, but it takes human verification to confirm if a provider truly delivers round-the-clock threat monitoring or merely resells basic firewall licenses.
Before making a purchase decision for any intelligence tool, ask your vendor a rigid set of qualification questions:
- Can I get a sample list?
- Can I filter by USA, Australia, Canada, or global markets?
- Can I separate MSSPs from general MSPs?
- Are security focus areas included?
- Is the data delivered in a usable format for CRM or campaign tools?
- Does the provider explain privacy, compliance, and opt-out processes?
- Is there a human team available for custom research?
Why Would a Buyer Choose DiscoverMSPs If It Is Newer in the Market?
It is a fair question from a cautious buyer. Procurement teams often lean towards legacy providers out of habit, but newness is not automatically a weakness in the data industry. In specialist markets, older tools frequently suffer from technical debt and outdated categorisation models that struggle to keep pace with how modern managed security service providers actually label themselves today. A legacy system might force an advanced threat intelligence consultancy into the exact same category as a local printer repair shop.
A newer platform may be built more directly around current channel behaviour, offering the specific segmentation and fresher buyer intent signals that older directories simply never coded into their original architecture. Market agility matters when targeting an mssp usa, because the terminology and service offerings evolve constantly. Still, as a buyer, your responsibility remains the same. You should verify all platform claims through sample data, candid conversations with the provider, and rigorous data-fit testing against your own sales objectives.
Trust also depends on privacy. Any serious buyer needs to understand what happens to customer data, contact data, and compliance responsibilities after purchase.
How Does DiscoverMSPs Handle Privacy If You Purchase MSSP Data?
Acquiring contact information for potential partners is only the beginning of a data lifecycle. Responsible B2B data use is not just about buying a list. It is fundamentally about how the buyer stores, segments, contacts, suppresses, and updates that data within their own systems. For this reason, channel leaders and procurement teams should review the Privacy Policy and the GDPR Compliance Policy directly before authorising a purchase. A vendor must ensure their own internal governance aligns with how the intelligence was gathered.
To provide clear context, the DiscoverMSPs Privacy Policy states that it collects personal and non-personal information. The organisation may use this data to provide and improve services, respond to enquiries, send communications with consent where required, monitor site performance and security, and comply with strict legal obligations. Furthermore, it states that users may have rights to access, correct, delete, or opt out depending on their geographic location. This transparency is critical. If your compliance or legal teams need further clarification on how data points align with your internal risk frameworks, you should Contact DiscoverMSPs to ask specific questions before executing a campaign.
What Responsible Buyers Should Do After Receiving MSSP Data
The moment a data file is transferred, the responsibility for its ethical use shifts to your revenue and marketing teams. To maintain compliance and protect your domain reputation, your operational workflow must be meticulous.
- Store the data securely.
- Import it only into approved CRM or campaign systems.
- Keep opt-out and suppression lists active.
- Tailor outreach to what matters to each firm, not just volume.
- Avoid contacting roles that are clearly outside the campaign purpose.
- Respect regional rules across USA, Canada, Australia, the UK, and other markets.
- Recheck data freshness before major campaign launches.
- Ask the provider how sample records, custom fields, and refresh cycles work.
What Makes an MSSP List Useful for Sales, Partnerships, and Market Research?
The true value of a targeted dataset depends entirely on who is looking at it. A single list of managed security service providers serves entirely different strategic functions across an organisation. For sales teams, the list helps prioritise outreach, allowing account executives to bypass generalist IT shops and focus immediately on mature security operators. For channel teams, it acts as a foundation for partner recruitment, helping managers identify the exact firms that possess the technical capacity to deploy complex solutions.
It is useful beyond outreach too. For investors and private equity, this data maps a market and shows mergers and regional leaders. For tech vendors, it finds the top managed security service providers likely to resell, integrate or recommend their tools to clients. One accurate data source keeps every team working from the same facts.
A high-quality list of managed security service providers should support:
- Territory planning
- Partner recruitment
- Account-based marketing
- Vendor alliance research
- Cybersecurity channel expansion
- Market mapping
- Competitive intelligence
- Local and global campaign segmentation
Where Do USA, Australia, Canada, and Global MSSP Markets Fit?
When mapping a global channel strategy, geography dictates demand. Finding mssp companies in usa is often the first priority for technology vendors because of the unmatched market size, high cybersecurity spending, dense vendor concentration, and overall channel maturity. The American market sets the pace for managed security adoption, making it the most competitive but potentially most lucrative region for a software vendor to establish a foothold. However, building an exclusive focus on an mssp usa search ignores massive opportunities in adjacent markets.
Australia and Canada matter a lot to global channel plans. Many providers there serve regulated sectors, strong mid-size firms and growing small firms with rising cloud security needs. Both countries have mature rules that push firms to outsource security. Global coverage matters for vendors that sell across regions or want partners in several countries at once. A full data platform lets a channel chief spread effort sensibly across these markets.
By this point, the buyer has a framework. The final step is turning that framework into a practical shortlist and knowing when to speak with a data team.
How to Build a Better MSSP Shortlist Without Losing Weeks
When you are responsible for channel growth or B2B customer acquisition, your pipeline depends entirely on how quickly you can move from a broad list of names to a functional, highly qualified shortlist. The most efficient revenue teams do not guess their way through this process. They follow a deliberate, repeatable strategy to ensure every hour spent on outreach targets an ideal partner profile.
To build a high-converting segment without draining your administrative resources, use this structured approach:
- Define the exact MSSP profile you need.
- Choose priority regions such as USA, Australia, Canada, and global markets.
- Decide whether you need pure MSSPs, hybrid MSP-MSSPs, MDR providers, SOC partners, compliance-focused firms, or cloud security specialists.
- Review sample records before buying a full list.
- Check whether the list includes company, service, location, size, and contact-level context.
- Match the data to your campaign purpose.
- Keep privacy, consent, opt-out, and suppression processes ready before outreach.
- Measure campaign quality by relevance, not just list volume.
When Should You Speak With a Data Team?
Self-service filters are great for standard audience mapping. But complex campaigns reach a point where human judgement is needed. Talk to a data specialist when your outreach depends on several overlapping criteria. Perhaps your product must link deeply with certain SIEM tools. Or your territory plan needs a strict mix of region, team size and niche compliance skills. Then a direct chat with an analyst is worth a lot.
Speaking with a specialist team prevents you from making faulty assumptions about your target market. When you choose to Contact DiscoverMSPs, you can request a targeted sample or discuss your precise ideal customer profile parameters in detail. This ensures that the data delivered to your revenue operations team matches the real-world operational realities of the providers you are trying to acquire.
Final Thoughts
Finding mssp companies in usa is not about collecting the biggest spreadsheet. It is about knowing which managed security service providers match the market, the offer, and the commercial goal. The right list should reduce uncertainty, not create more clean-up work for your sales development representatives.
For software vendors, institutional investors, and channel teams, a specialist platform can make the difference between broad, generic outreach and a sharper, more profitable market entry. Investing in verified intelligence upfront protects your brand equity and ensures your sales pipeline is built on a foundation of genuine operational fit.
FAQs About Finding MSSP Companies in USA and Worldwide
1. What is the best way to find MSSP companies in USA?
Use a verified database built for the channel, not broad web searches or generic business directories. Make sure you can filter by proven security skills, local presence, client size and current tech links. Always ask for sample records and check how deep the data goes before you spend your budget.
2. What is the difference between MSPs and MSSPs?
MSPs usually focus on broad IT: infrastructure, help desk, network uptime and basic cloud admin. MSSPs focus only on cutting cyber risk. Their main services usually include running a security operations centre, MDR, endpoint protection, deep vulnerability management, compliance and incident response.
3. Why should I use a list of managed security service providers instead of manual research?
Manual research is incredibly slow, inconsistent, and highly prone to human error. Website copy can be misleading, often causing general IT firms to look like advanced security providers on the surface. A verified, structured list provides pre-vetted service-level detail, technographic insight, and accurate firmographic context. This allows your team to skip the time-consuming process of website auditing and focus directly on strategic analysis and outreach.
4. Can I find top managed security service providers by country?
Yes, provided your data intelligence platform supports rigorous country-level and regional filtering. High-quality channel data should allow you to segment providers across the USA, Australia, Canada, the UK, and global markets. This ensures you can easily align your partner recruitment or sales campaigns with specific regional compliance laws and geographic territory structures.
5. How do I know if DiscoverMSPs is the right option?
Judge the platform on your exact needs. Read its managed security service providers database page, ask for a targeted sample and compare the fields against your ideal customer profile. Check how fresh the data is, how it is checked and how it handles privacy, so it supports your campaigns safely.
To start with a cleaner shortlist, review the managed security service providers database on DiscoverMSPs or contact the team for a sample matched to your target market.
Frequently Asked Questions
How accurate is DiscoverMSPs' data?
How often is DiscoverMSPs' data refreshed?
Can I get a free sample before committing?
Is DiscoverMSPs' data compliant with outbound marketing regulations?
How quickly can I get a custom data list from DiscoverMSPs?
Does DiscoverMSPs offer data outside the USA?
How to Build a Better MSSP Shortlist Without Losing Weeks
An eight-step repeatable strategy for revenue operations, channel, and partner recruitment teams to build a high-converting MSSP shortlist efficiently.
Define the exact MSSP profile you need
Before opening any database, document your ideal partner profile in detail. Specify whether you need a pure MSSP, a hybrid MSP-MSSP, a dedicated MDR provider, a SOC partner, a compliance-focused firm, or a cloud security specialist. Precision at this stage eliminates a large proportion of irrelevant outreach before a single email is sent.
Choose priority regions including USA, Australia, Canada, and global markets
Identify which geographic markets are critical to your channel strategy and assign them in order of commercial priority. Different regions carry distinct regulatory requirements, market maturity levels, and competitive dynamics. Aligning your data request to specific countries prevents your sales team from working across incompatible compliance frameworks simultaneously.
Segment by security specialisation and service focus
Decide whether your campaign targets pure MSSPs, hybrid MSP-MSSPs, MDR providers, SOC partners, compliance-focused firms, or cloud security specialists. These categories represent completely different business models, buyer needs, and commercial conversations. Mixing them into a single undifferentiated list will undermine your messaging relevance and dramatically reduce your campaign conversion rates.
Review sample records before buying a full list
Request a sample dataset filtered to your exact ideal customer profile before committing your budget. Review the field structure, data depth, and accuracy of the records against known providers in your target market. A platform that refuses to provide a sample before purchase is signalling a lack of confidence in their own data quality.
Check that the list includes company, service, location, size, and contact-level context
Verify that the data goes beyond basic company names and websites. A useful MSSP list should include verified geographic location, precise employee size, specific security service categories, decision-maker contacts where available, and CRM-ready formatting. Without this depth, your sales team will still spend hours manually auditing websites before writing a single personalised email.
Match the data to your specific campaign purpose
Confirm that the available data fields directly support your intended use case, whether that is partner recruitment, direct sales, account-based marketing, investment research, or competitive intelligence. A dataset optimised for partner recruitment may lack the granular technographic signals needed for competitive displacement campaigns and vice versa.
Prepare privacy, consent, opt-out, and suppression processes before outreach
Before a single email is sent, ensure your internal data governance framework is fully operational. Set up suppression lists, configure opt-out management, and confirm that your outreach templates comply with applicable regional privacy laws including GDPR, CCPA, CASL, and Australian Privacy Act requirements. Compliance failures at this stage can result in severe reputational and financial damage.
Measure campaign quality by relevance, not just list volume
After launching your first outreach sequence, measure success by response quality, meeting conversion rate, and partner qualification rate rather than raw list size. A targeted list of five hundred highly relevant MSSP firms will consistently outperform a generic list of five thousand unqualified contacts. Regularly feed performance data back into your segmentation criteria to continuously improve shortlist precision.
 ChatGPT
 Claude
 Google AI Mode