The United States is home to more managed service providers than any other country in the world. US MSPs range from two-person boutique providers serving local small businesses to national organizations managing IT for thousands of enterprise clients simultaneously. For a business looking to engage managed IT services in the USA, this abundance of options is simultaneously useful and overwhelming.
The provider who is right for a 20-person healthcare practice in Nashville is not the same as the right provider for a 500-person defense contractor in Northern Virginia, even though both might describe themselves as full-service managed IT service providers using identical marketing language.
This guide cuts through that noise. It covers what managed IT services in the USA actually include across the current market, how costs vary by region and service scope, which compliance frameworks shape provider selection in regulated industries, and how to find verified US managed IT service providers without relying on search engine results that reward marketing spend over service quality. The DiscoverMSPs US managed IT services directory covers verified providers across all major US markets.
What Managed IT Services in the USA Actually Include
The scope of what US managed IT service providers deliver has expanded substantially over the past decade. Understanding the full spectrum of available services allows businesses to articulate their requirements precisely rather than accepting whatever a provider’s default package includes.
Core infrastructure management
The base layer of any US managed IT services contract covers network monitoring, server and device management, patching for operating systems and apps, backup and disaster recovery, and help desk support. Almost every US MSP offers this base package. But quality varies a lot. A provider that patches on a set schedule is managing risk. One that patches only after a flaw is being exploited in public is managing damage.
Cybersecurity services
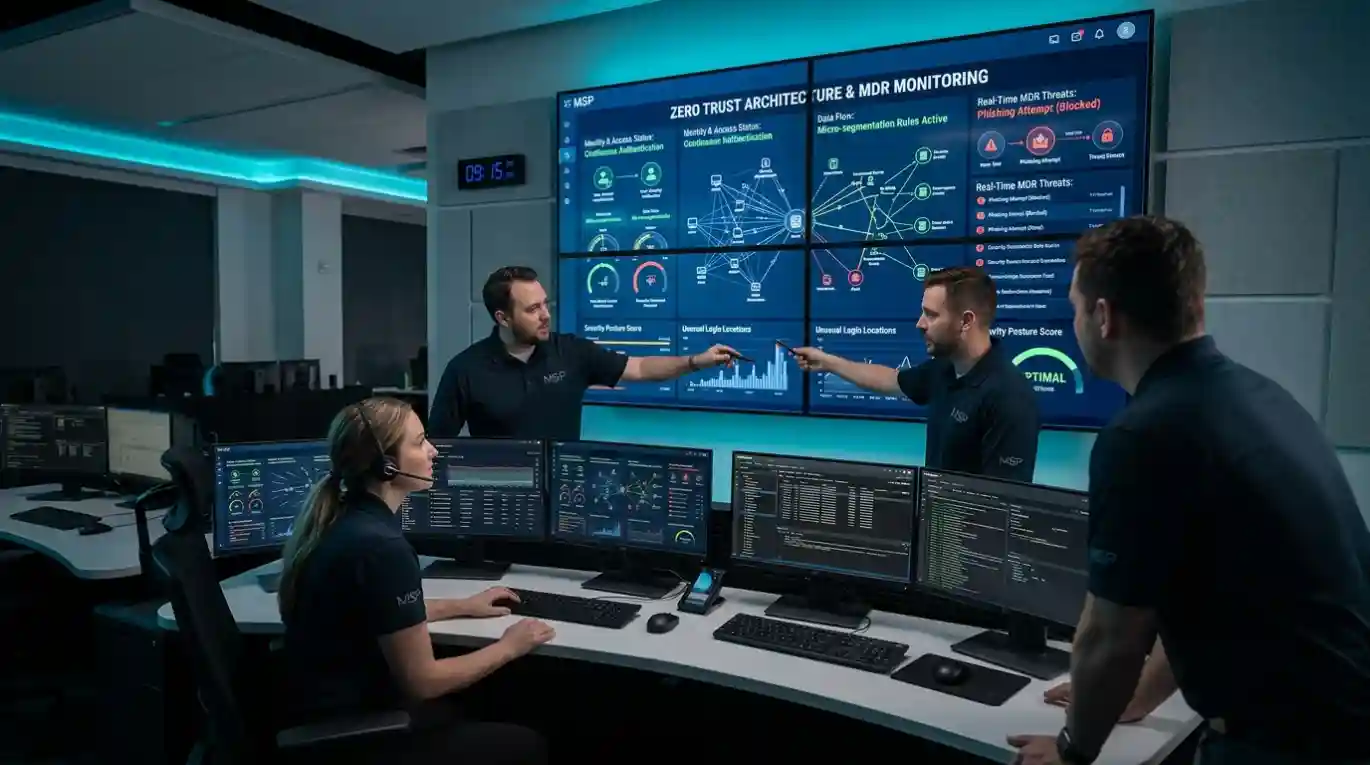
Cybersecurity is now the main driver of growth in US managed IT services. US MSPs now include endpoint detection and response, email security, vulnerability management, SOC-as-a-service, penetration test coordination and vCISO services in their managed IT packages. Firms that buy security separately from managed IT create a gap between running their systems and watching them for threats. Attackers look for exactly that gap.
Compliance program management
US tech regulation is among the most complex in the world. Federal rules like HIPAA, CMMC and GLBA sit alongside state rules, including California's CCPA, New York's NYDFS Cybersecurity Regulation and a growing list of state privacy laws. The best US managed IT service providers build compliance into their services rather than billing it as a separate project. Compliance-focused US managed IT service providers that deliver it as part of the service get clearly better results than those that treat it as an afterthought.
Managed IT Services Costs in the USA: What to Expect by Region and Sector
Pricing for managed IT services in the USA varies by service scope, geographic market, and industry vertical in ways that make direct price comparisons unreliable without understanding the variables driving the difference.
Geographic pricing variation
US managed IT service providers in major metropolitan markets including New York, San Francisco, Boston, and Washington DC command higher per-user rates than equivalent providers in mid-tier markets. This reflects both higher local operating costs and the premium that compliance-intensive industries concentrated in these cities are willing to pay for verified expertise. A New York financial services MSP with demonstrated NYDFS compliance capability commands $200 to $300 per user per month for a full-service engagement.
Healthcare MSPs with real HIPAA skills charge more than generalists of the same technical quality. Defence MSPs with CMMC certification also charge more, reflecting the large cost of getting and keeping it. These higher prices are fair. The compliance skills behind them really do lower client risk in ways a cheaper generalist cannot. The vertical-specific IT services directory on DiscoverMSPs covers US providers with proven industry focus across healthcare, finance, law, manufacturing and defence.
Looking for a verified managed IT services provider in the USA? Browse the DiscoverMSPs US directory to compare providers by region, vertical, and compliance specialization.
The Compliance Frameworks That Shape US MSP Selection
The US regulatory environment for managed IT services is more fragmented than most other markets because compliance obligations vary significantly by industry and increasingly by state. Understanding which frameworks apply to your business is the first step toward identifying which US managed IT service providers are genuinely equipped to serve you.
HIPAA for healthcare
Any managed IT service provider serving healthcare firms that hold protected health information (PHI) must act as a HIPAA Business Associate. It must sign a Business Associate Agreement (BAA) with the client. HIPAA compliance for managed IT covers technical safeguards, such as access controls, audit logs and secure data transfer. It covers physical safeguards for any systems that hold PHI. And it covers admin safeguards, such as staff training and incident response steps. A US healthcare MSP that cannot show its own HIPAA papers and a sound BAA template is not ready to serve regulated healthcare clients.
CMMC for defense contractors
The Cybersecurity Maturity Model Certification has expanded the compliance requirements for US defense contractors in ways that are reshaping the US managed IT services market. CMMC Level 2 requires third-party assessment for contractors handling Controlled Unclassified Information. US managed IT service providers who serve the defense industrial base must either hold CMMC certification themselves or demonstrate the specific technical controls required by NIST SP 800-171 as part of their service delivery architecture. The NIST SP 800-171 security requirements provide the technical baseline for evaluating a US MSP’s CMMC readiness.
SOC 2 and the technology sector
SOC 2 Type II has become a basic must for US tech firms that serve large clients. Managed IT service providers that run systems for SaaS firms, tech platforms and data-heavy businesses are more and more expected to hold SOC 2 Type II themselves. It shows the provider's own systems meet the security and uptime standards their clients' customers demand. US MSPs without SOC 2 are at a growing disadvantage with enterprise tech accounts.
How to Find Verified US Managed IT Service Providers
The US managed IT services market’s size and marketing sophistication make it particularly difficult to evaluate providers from search engine results alone. Providers who rank highly in Google searches for “managed IT services USA” or “best MSP near me” are often those who have invested most in SEO and paid search, not those who deliver the best services. This disconnect between marketing visibility and service quality is more pronounced in the US market than in most other countries, simply because the market’s size and competitive density create strong incentives for marketing investment that does not necessarily correspond to service investment.
Verified provider data that goes beyond marketing claims is the only reliable starting point for US MSP selection. The DiscoverMSPs database covers over 40,000 verified US managed IT service providers with technographic data on current technology stacks, firmographic data on company size and geography, and contact intelligence for the decision-makers who manage client relationships. This intelligence allows businesses to shortlist providers who actually match their requirements rather than those who most aggressively market to their search queries.
Frequently Asked Questions
How accurate is DiscoverMSPs’ data?
How often is DiscoverMSPs’ data refreshed?
1.What do managed IT services in the USA typically include?
Managed IT services in the USA usually include network monitoring, help desk support, device security, patching, cloud management, backup and disaster recovery, and compliance support. Leading US managed service providers also offer security operations through SOC-as-a-service, vCISO services and compliance programmes for HIPAA, SOC 2, CMMC and NIST CSF. The exact scope varies a lot by provider and contract tier.
2.How much do managed IT services cost in the USA?
Managed IT services in the USA typically cost between $100 and $250 per user per month for fully managed services. Infrastructure-only management starts lower. Compliance-heavy packages for regulated industries and full-stack cybersecurity services sit at the higher end. Geographic variation is significant: MSPs in New York, San Francisco, and Boston command higher rates than equivalent providers in mid-tier US cities, reflecting both higher operating costs and compliance expertise premiums.
3.What compliance frameworks do US managed IT service providers support?
US managed IT service providers support frameworks depending on their vertical specialization. Healthcare-focused MSPs deliver HIPAA compliance management. Financial services MSPs support SOC 2 and GLBA. Defense industry MSPs are increasingly CMMC-certified. Federal contractor MSPs align with NIST SP 800-171. Horizontal frameworks including SOC 2 Type II and ISO 27001 are relevant across most regulated sectors and serve as baseline quality indicators across the US market.
4.How do I choose the right managed IT services provider in the USA?
Start with industry focus. A US MSP with deep experience in your industry brings ready-made compliance processes and app know-how a generalist cannot match. Then check the SLA terms, references from current clients of your size, and whether the pricing model fits. Use the DiscoverMSPs directory to find checked US providers by region, industry and tech stack before you start a formal review.
5.What is CMMC and which US managed IT service providers offer it?
The Cybersecurity Maturity Model Certification (CMMC) applies to US defence contractors that handle Controlled Unclassified Information. CMMC Level 2 needs an outside assessment. US managed IT service providers serving defence suppliers must either hold CMMC themselves or support their clients through it. Demand for CMMC-ready MSPs has grown a lot as the Department of Defense has added the rule to more types of contract.
6.What is the difference between an MSP and an MSSP in the USA?
In the US market, a managed service provider focuses on running IT systems and general IT management. A managed security service provider specializes in cybersecurity: SOC monitoring, threat detection, incident response and compliance security controls. Many US providers now offer both. The difference matters most when a business has security or compliance needs beyond what a general IT provider can deliver.
The Right US MSP Changes What Your Business Can Accomplish
Managed IT services in the USA at their best are not a support function. They are the infrastructure that allows a business to scale, meet compliance obligations, and compete with organizations that have significantly larger internal IT resources. The right US managed IT service provider gives a 50-person company the IT reliability and security posture of a 500-person company. The wrong one gives them a support ticket queue and a monthly invoice.
The distinction between those two outcomes is made in the selection process, not during the contract. Businesses that invest in rigorous provider evaluation, using verified data rather than search engine rankings, consistently report better service quality, lower total IT costs, and stronger compliance outcomes than those who select on price alone or based on whoever called them first.
DiscoverMSPs provides the verified US managed IT service provider intelligence that makes the selection process faster, more reliable, and less dependent on marketing claims. Over 40,000 verified US providers, segmented by geography, vertical, certification, and technology stack. Start there.
 ChatGPT
 Claude
 Google AI Mode